Uploaded image for project: 'OpenId Connect'
  1. OpenId Connect
  2. OIDC-283

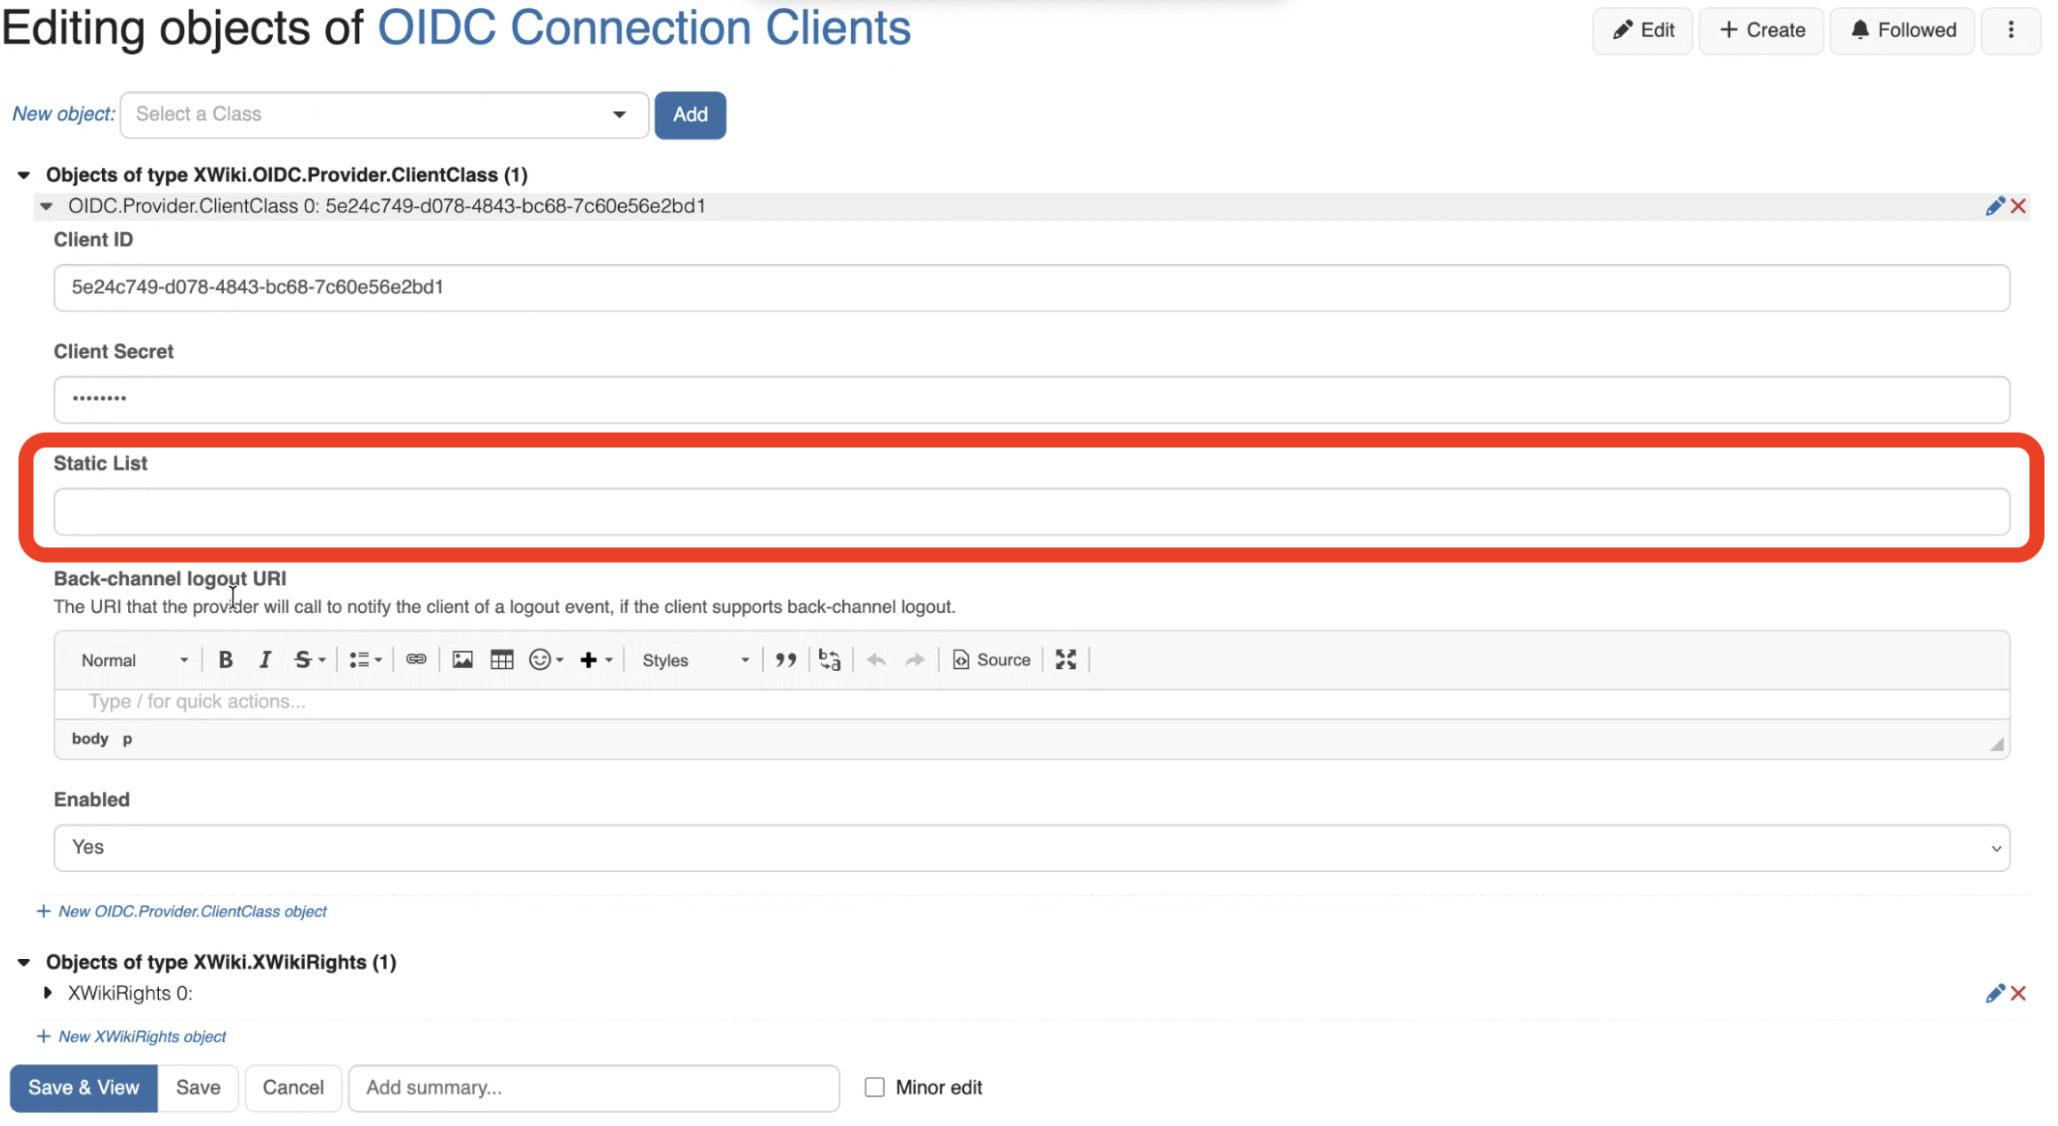
Allow registering relying parties

    XMLWordPrintable

Details

    • New Feature
    • Resolution: Fixed
    • Major
    • 2.21.0
    • 2.20.3
    • Provider
    • None
    • Integration
    • Unknown
    • N/A
    • N/A

    Description

      Right now the provider does not provide any way to verify the relying party, only the user and token.

      Being able to limit access to specific clients only would straighten security and reduce the impact of a stolen access token.

      Even if it's not mandatory in the core OIDC protocol, it's becoming more and more the norm in OIDC providers.

      Attachments

        1. oauth_setup.png
          420 kB
          Dominic Bräunlein

        Issue Links

          Activity

            People

              tmortagne Thomas Mortagne
              tmortagne Thomas Mortagne
              Votes:
              0 Vote for this issue
              Watchers:
              1 Start watching this issue

              Dates

                Created:
                Updated:
                Resolved: